--- title: "ADFS with OpenID SSO" slug: "adfs-with-openid-sso" description: "Set up Single Sign-On between Document360 and ADFS using OpenID with our step-by-step guide for seamless user access and security." updated: 2026-06-19T08:50:00Z published: 2026-06-19T08:50:00Z canonical: "docs.document360.com/adfs-with-openid-sso" --- > ## Documentation Index > Fetch the complete documentation index at: https://docs.document360.com/llms.txt > Use this file to discover all available pages before exploring further. # ADFS with OpenID SSO **Active Directory Federation Services (ADFS)** is Microsoft's on-premises identity provider that enables federated identity and single sign-on across applications. With OpenID Connect SSO configured between ADFS and Document360, your users and readers can sign in to Document360 using their existing Active Directory credentials. :::(Info) ( NOTE) Only users with the **Owner** or **Admin** project role can configure SSO in Document360. ::: ## What you can do with ADFS as your IdP | Capability | Supported | |---|---| | User (portal) authentication | Yes | | Reader (knowledge base site) authentication | Yes | | SCIM provisioning | Yes (via third-party tools or custom integrations only) | | SSO configuration inheritance (parent-child projects) | Yes | --- ## Before you begin - You have administrative access to both Document360 and your ADFS server. - You have **Owner** or **Admin** access in your Document360 project. - Open Document360 and ADFS in two separate browser tabs before starting. --- ## How to configure ADFS OpenID SSO in Document360 ### Step 1: Add the application in ADFS 1. Log in to the **ADFS Management** console on your ADFS server. 2. In the ADFS Management console, navigate to **Relying Party Trusts**. 3. Right-click **Relying Party Trusts** and select **Add Relying Party Trust**. 4. In the **Add Relying Party Trust Wizard**, choose **Claims aware** and click **Start**. 5. Select **Enter data about the relying party manually** and click **Next**. 6. Provide a display name (for example, "Document360 OpenID SSO") and click **Next**. 7. In the **Configure Certificate** step, click **Next** (you can skip this if not using a certificate). --- ### Step 2: Get the SP parameters from Document360 1. Open Document360 in a separate tab. 2. Navigate to **Settings** () > **Users & permissions** > **SSO Configuration**. 3. Click **Create SSO**.
Settings page displaying SSO configuration options and user permissions for identity providers.
4. Select **ADFS** as your identity provider to navigate to the **Configure the Service Provider (SP)** page automatically.
Select an Identity Provider for SSO configuration, highlighting ADFS option prominently.
5. On the **Configure the Service Provider (SP)** page, select the **OpenID** radio button. 6. A set of parameters will be displayed.
Configuration settings for OpenID in the Service Provider setup for SSO.
--- ### Step 3: Enter the Document360 parameters in ADFS 1. Switch to the ADFS Management console tab and enter the Document360 parameters into the corresponding fields in the **Configure URL** step using the mapping below. | ADFS | Document360 | |---|---| | Relying Party Identifier | Subdomain name | | Sign-On URL | Sign in redirect URL | | Sign-Out URL | Sign out redirect URL | 2. Click **Next** and complete the remaining steps in the wizard, such as setting up multi-factor authentication if required, and permitting all users to access the application. 3. Review your settings and click **Next** to add the relying party trust. 4. On the final screen, check the box for **Open the Edit Claim Rules dialog** and click **Close**. --- ### Step 4: Add claim rules in ADFS 1. In the **Edit Claim Rules** dialog, click **Add Rule**. 2. Select **Send LDAP Attributes as Claims** as the rule template and click **Next**. 3. Provide a name for the claim rule (for example, "Send LDAP Attributes"). 4. Configure the following: - **Attribute Store**: Select **Active Directory**. - **Mapping**: - **LDAP Attribute**: User-Principal-Name | **Outgoing Claim Type**: Name ID - **LDAP Attribute**: E-Mail-Addresses | **Outgoing Claim Type**: Email - **LDAP Attribute**: Display-Name | **Outgoing Claim Type**: Name 5. Click **Finish** to add the rule. 6. Click **Apply** to save your changes and close the dialog. --- ### Step 5: Configure the Identity Provider in Document360 1. Return to Document360 on the **Configure the Service Provider (SP)** page and click **Next** to navigate to the **Configure the Identity Provider (IdP)** page. 2. Enter the corresponding values from your ADFS configuration using the mapping below. | ADFS | Document360 | |---|---| | Client Identifier (Client ID) | Client ID | | Client Secret | Client Secret | | Issuer URL | Authority (Authorization URL or Endpoint) | :::(Info) ( NOTE) Ensure that the **Client ID** in Document360 matches the **Relying Party Identifier** configured in ADFS. ::: 3. In the **Scope** (optional) field, type a scope value and click **+** to add it as a chip. This defines what user information or permissions Document360 requests from ADFS. You can add up to 3 scopes.
Configure the Identity Provider page for ADFS OpenID Connect in Document360.
4. Click **Next** to proceed to the **SCIM provisioning** page. --- ### Step 6: Configure SCIM provisioning SCIM provisioning allows you to automate user and reader lifecycle management between ADFS and Document360. Since ADFS does not natively support SCIM, this requires a third-party tool or a custom-built integration. If you do not need SCIM provisioning, skip to [Step 7: Configure SSO name and login options](#step-7-configure-sso-name-and-login-options). 1. Turn on the **Enable SCIM provisioning** toggle.
Instructions for enabling SCIM provisioning in Document360 for user synchronization.
2. A confirmation dialog appears. Review the terms, select the checkbox, and click **Agree**. 3. The parameters required to complete the SCIM configuration will then be displayed. :::(Info) ( NOTE) SCIM provisioning in ADFS can be enabled using third-party tools or custom-built integrations only. ADFS does not natively support SCIM provisioning. ::: 4. Enter the required parameters from Document360 into the corresponding fields in your custom app.
Configuration settings for SCIM provisioning and identity provider setup in a web interface.
5. In the **Default role** field, the role is set to **Contributor** by default. You can change this from the dropdown if needed. 6. In the **User groups** and **Reader groups** fields, select the groups you want to add. Multiple groups can be added, and they will inherit the default role you selected earlier. 7. Click **Next** to navigate to the **More settings** page. --- ### Step 7: Configure SSO name and login options 1. In the **SSO name** field, enter a name for the SSO configuration. 2. In **Customize login button**, enter the text for the login button displayed to users. 3. [**Auto assign reader group**](https://docs.document360.com/docs/auto-assign-reader-group){target=`_blank`}: This option is only available for existing SSO configurations. For newly created SSO configurations, this toggle will not be displayed as SCIM automatically provisions users and groups. 4. Toggle **Sign out idle SSO user** on or off based on your requirements. 5. Choose whether to invite existing user and reader accounts to SSO.
Settings for creating a new SSO, including name and login button customization options.
6. Click **Create** to complete the OpenID SSO configuration. The SSO configuration using ADFS and the OpenID Connect protocol is now active in Document360. --- ## Managing users in ADFS To view readers added through your ADFS integration:
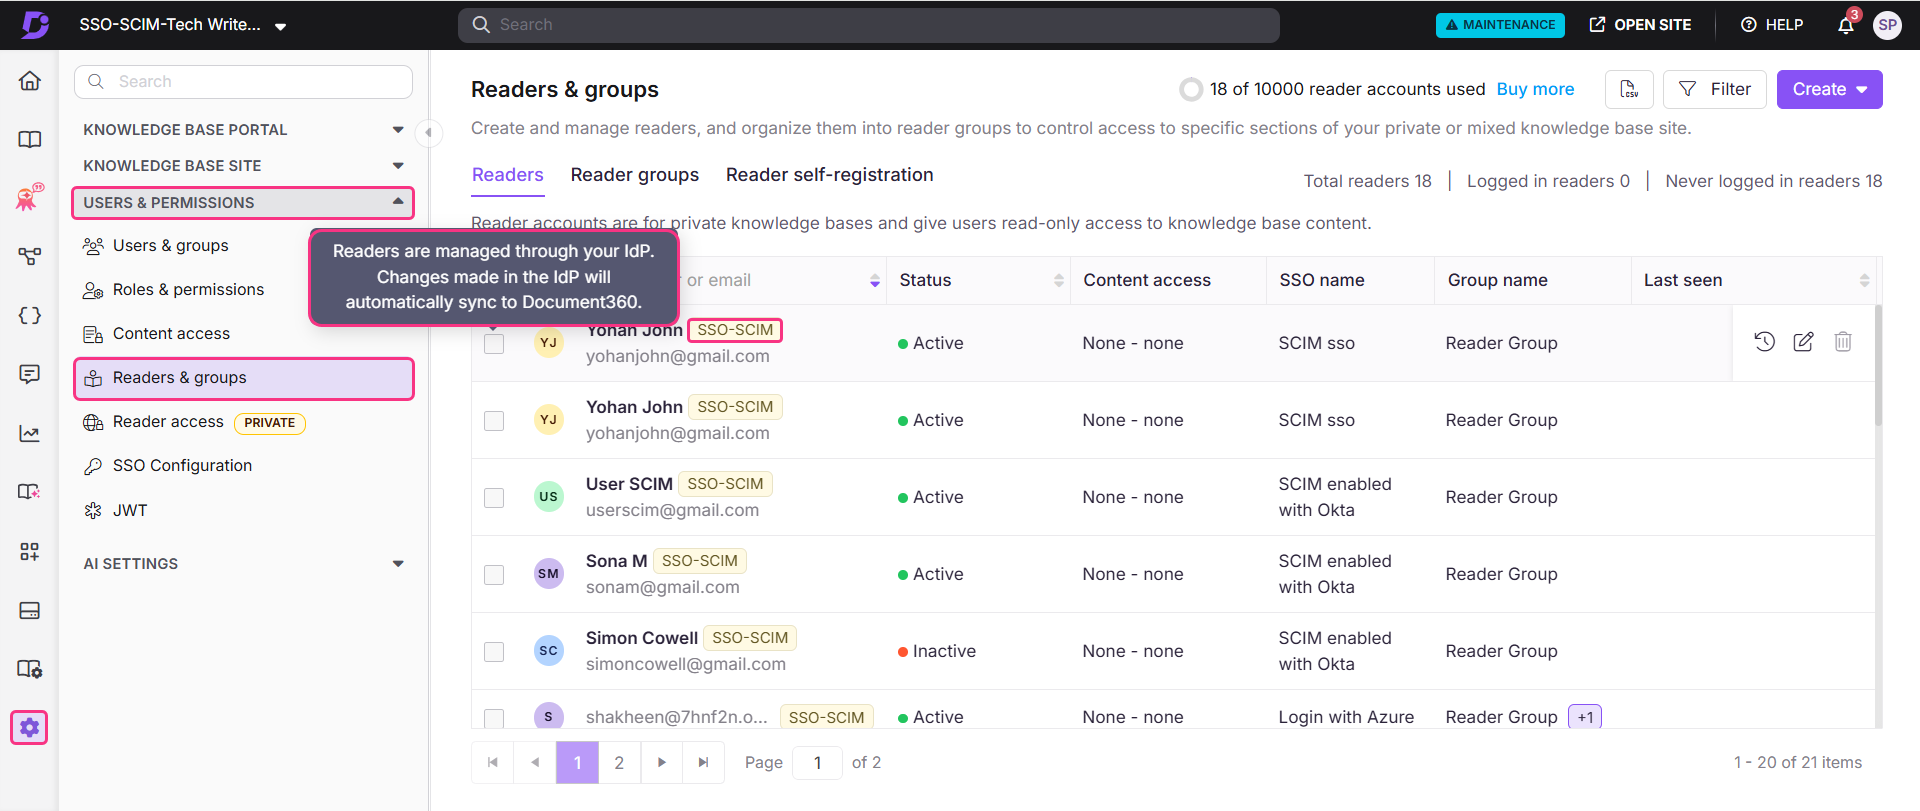
Overview of reader management settings, highlighting user accounts and permissions synchronization.
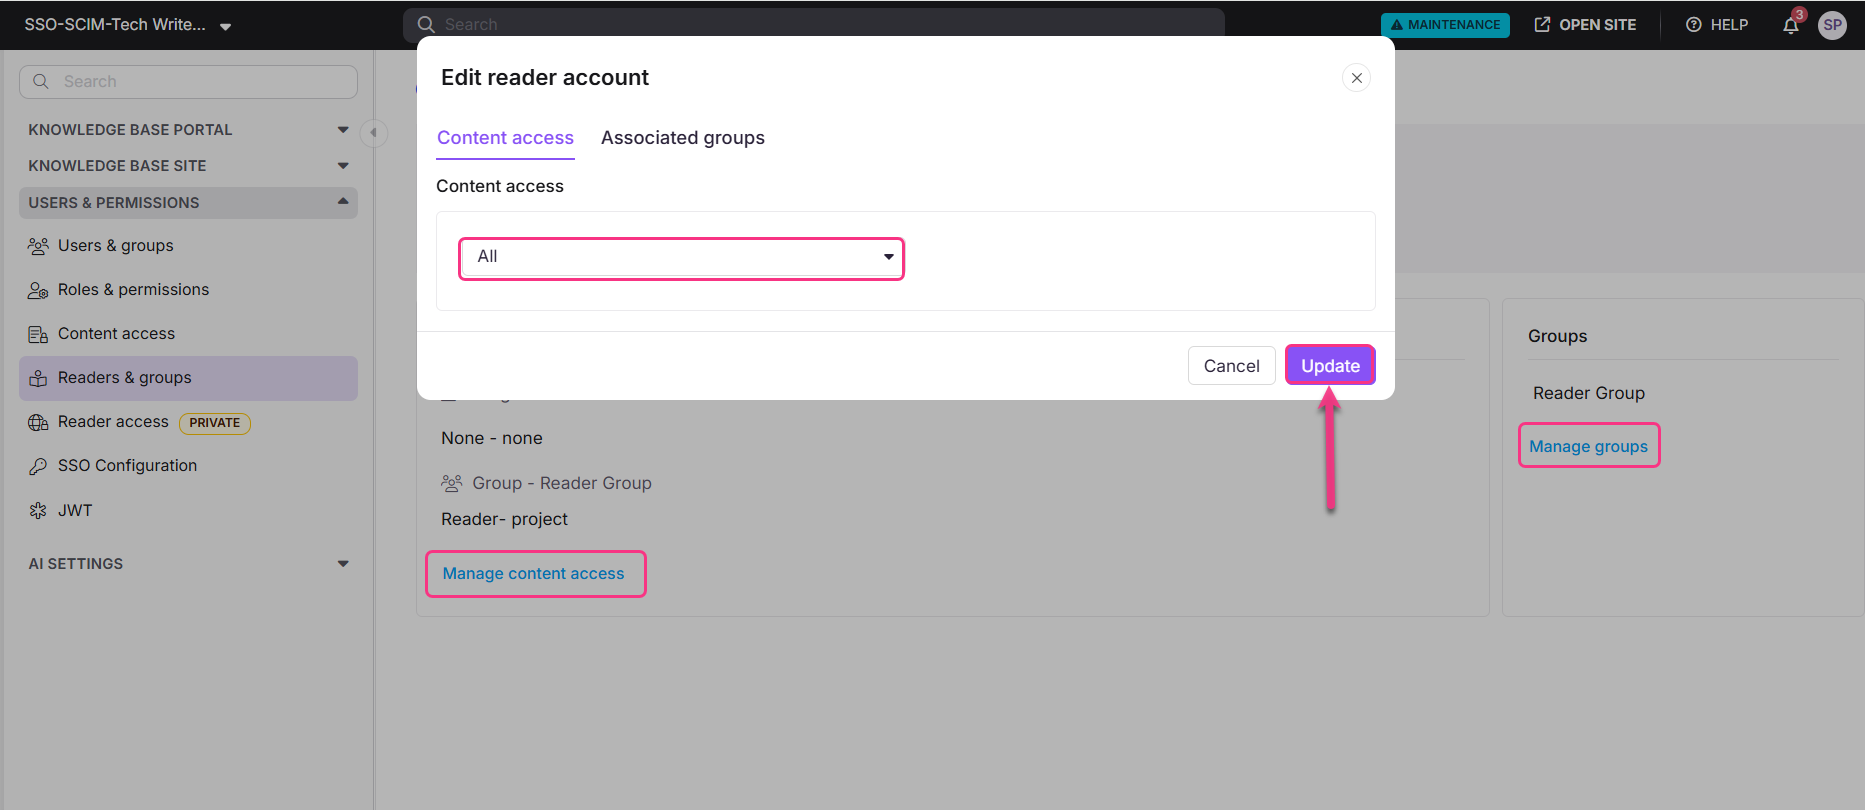
1. In Document360, navigate to **Settings** () > **Users & permissions** > **Readers & groups**. 2. Select the reader to navigate to their reader profile. Readers provisioned via SCIM will display an **SSO-SCIM** badge next to their name. :::(Info) ( NOTE) When SCIM is enabled, editing a user's name or deleting a user directly in Document360 is disabled, as these actions must be managed through your IdP to keep both platforms in sync. You can only manage content access from Document360. Deleting a profile in your IdP does not remove it from Document360 — the profile will remain with an Inactive status. ::: ### Manage content access of readers, users, and groups The default content role assigned to any new user, reader, or group is based on what was configured during SCIM provisioning setup. Permissions will be set to **None** by default but can be updated at any time. 1. Select the desired reader and click **Manage Content Access**. 2. Choose the desired access level from the dropdown and click **Update**.
Editing reader account settings, including content access and associated groups options.
--- ## Best practices - **Verify the Client ID matches the Relying Party Identifier.** The Client ID entered in Document360 must exactly match the Relying Party Identifier configured in ADFS. A mismatch will cause authentication failures. - **Use the correct outgoing claim type for email.** For OpenID Connect ADFS, the outgoing claim type for email is **Email**, not Email-Addresses as used in the SAML configuration. Using the wrong claim type will cause user identity errors. - **Use a third-party tool for SCIM.** ADFS does not natively support SCIM provisioning. Plan your user provisioning approach before enabling SCIM in Document360. - **Rotate client secrets before expiry.** The client secret configured in ADFS has an expiry date. When it expires, SSO authentication will fail. Monitor expiry and rotate secrets in advance. --- ## FAQ

Why is SCIM not natively supported in ADFS?

ADFS is an on-premises federation service built on SAML and WS-Federation protocols. It does not include a built-in SCIM endpoint. To use SCIM with ADFS in Document360, you need a third-party provisioning tool or a custom integration that bridges ADFS with the SCIM protocol.

What happens to a user's profile in Document360 if I delete them in ADFS?

Deleting a user profile in your IdP does not remove it from Document360. The profile will remain in Document360 with an Inactive status.

How is the ADFS OpenID claim rule mapping different from the SAML claim rule mapping?

The claim rule mapping for OpenID Connect ADFS uses Email as the outgoing claim type for email addresses, while the SAML configuration uses Email-Addresses. Ensure you use the correct claim type for whichever protocol you are configuring.