---
title: "Managing SSO readers and reader groups"
slug: "auto-assign-reader-group"
description: "Make use of the auto register option to skip the SSO readers addition step in Document360. This is applicable for SAML and OpenID."
tags: ["SSO"]
updated: 2026-09-10T03:59:53Z
published: 2026-09-10T03:59:53Z
canonical: "docs.document360.com/auto-assign-reader-group"
---
> ## Documentation Index
> Fetch the complete documentation index at: https://docs.document360.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Managing SSO readers and reader groups
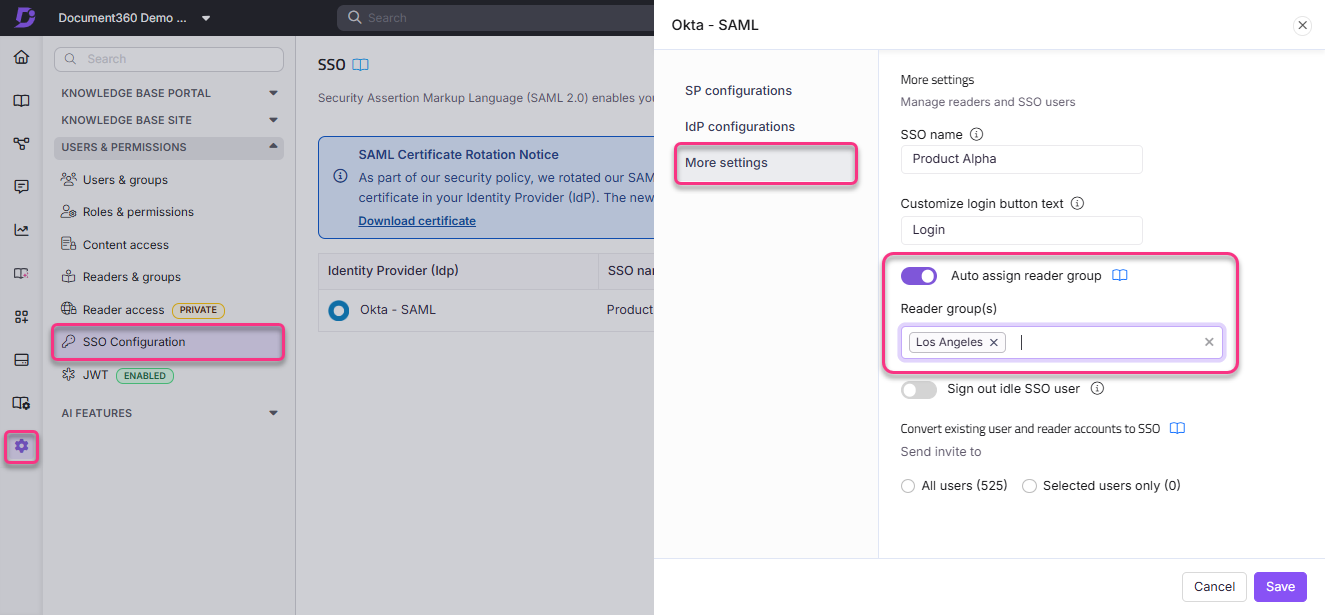
The **Auto assign reader group** feature in Document360 automatically grants knowledge base access to readers who sign in through an Identity Provider (IdP), without requiring you to invite them manually. When a reader authenticates via SSO for the first time, they are assigned to the reader groups you have pre-selected in the SSO configuration. This is especially useful for large or frequently changing user bases where readers are managed centrally in the IdP.
---
## Before you begin
- SSO must already be configured for your project using SAML or OpenID Connect.
- You must have existing reader groups set up in your project. If you have not created any yet, see [How to create a reader group](#how-to-create-a-reader-group) below.
- You must have the **Owner** or **Admin** project role to edit SSO configurations.
:::(Info) ( NOTE)
If your IdP does not support SCIM provisioning, contact the Document360 Support team to enable the **Auto assign reader group** feature for your account. To know about SCIM, read [SCIM provisioning](https://docs.document360.com/docs/scim-provisioning){target=`_blank`}.
:::
:::(Info) ( NOTE)
Auto assign reader group and SCIM provisioning cannot both be active on the same SSO configuration. If SCIM provisioning is enabled, use SCIM's own group sync to control which reader groups new SSO readers are added to. To use Auto assign reader group instead, contact [Contact Document360 support](https://document360.com/support){target=`_blank`} to have SCIM disabled for your project first.
:::
---
## How to enable auto assign reader group
1. Navigate to **Settings** () in the left navigation bar of the Knowledge base portal.
2. In the left navigation pane, go to **Users & permissions** > **SSO Configuration**.
3. Hover over the SSO configuration for which you want to enable auto assignment and click the **Edit** () icon.
4. In the SSO configuration panel, navigate to the **More settings** tab.
5. Turn on the **Auto assign reader group** toggle.
6. In the search field that appears, search for and select the reader groups you want to automatically assign to readers on login.
7. Click **Save**.
Readers who sign in via SSO will now be automatically assigned to the selected reader groups upon their first login.
---
## How to create a reader group
If you do not have any reader groups set up yet, you need to create them before enabling auto assignment.
1. Navigate to **Settings** () > **Users & permissions** > **Readers & groups** > **Reader groups**.
2. Click **New reader group** and enter the required details.
3. Click **Create reader group**.
Once the reader group is created, return to the SSO configuration and enable the **Auto assign reader group** option as described above. To know more, read [Create reader groups](https://docs.document360.com/docs/create-reader-group){target=`_blank`}.
---
## Best practices
- Assign readers to the most restrictive reader group by default. You can always grant additional access individually rather than opening up too much access automatically on first login.
- If your project serves multiple audiences (for example, internal staff and external customers), create separate reader groups for each and configure auto assignment per SSO configuration accordingly.
- Review your auto-assigned reader groups periodically to ensure they reflect your current access control requirements, especially after organizational changes in your IdP.
## Related
- [SAML SSO with Entra](/saml-sso-with-entra.md)
- [SAML SSO with OneLogin](/saml-sso-with-onelogin.md)
- [SAML SSO with other configurations](/saml-sso-with-other-configurations.md)