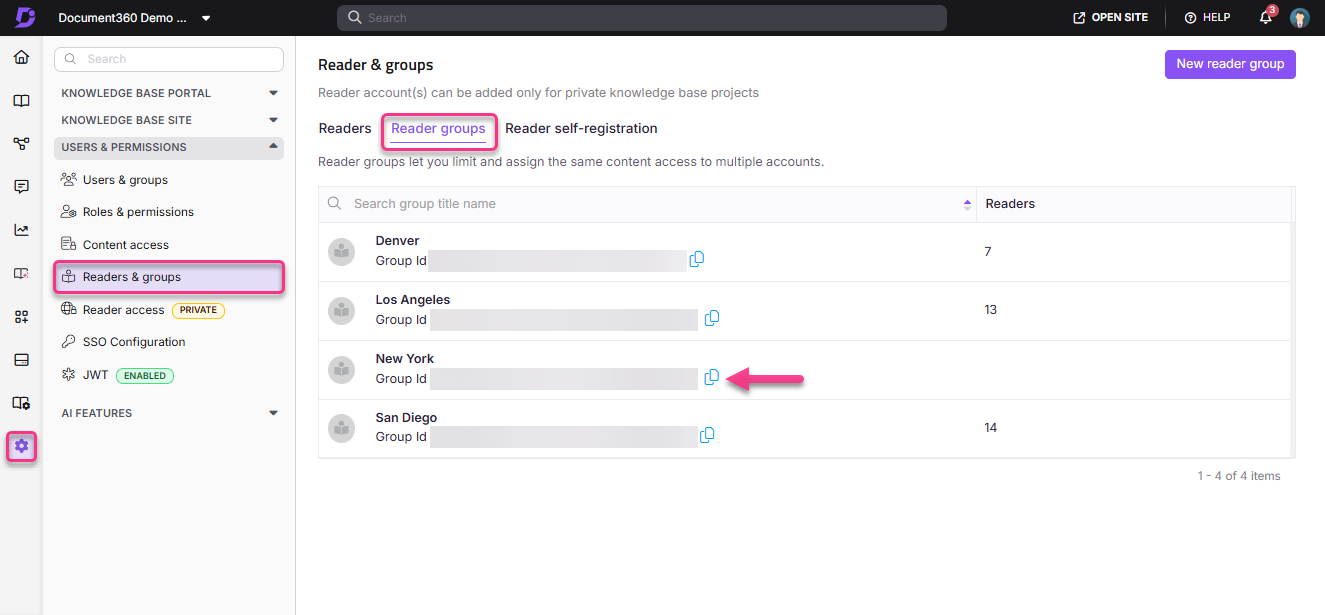
--- title: "JWT reader groups in your Document360 Knowledge base" slug: "jwt-reader-groups" description: "The JWT reader accounts can be associated with any existing reader groups on the Document360 project.The group restrictions can be applied to access specific content in the knowledge base." tags: ["JWT"] updated: 2026-08-19T04:27:41Z published: 2026-08-19T04:27:41Z canonical: "docs.document360.com/jwt-reader-groups" --- > ## Documentation Index > Fetch the complete documentation index at: https://docs.document360.com/llms.txt > Use this file to discover all available pages before exploring further. # JWT reader groups JWT reader groups let you control which sections of your private knowledge base each authenticated reader can access. When a reader logs in through JWT SSO, Document360 uses the reader group IDs in their token payload to determine which project versions, languages, categories, and articles they are allowed to view. A JWT reader group is identical to a regular Document360 reader group. It inherits the same restriction settings. The only difference is how assignment works: instead of manually assigning readers in the portal, you pass their group IDs directly in the JWT payload. --- ## When to use JWT reader groups Use JWT reader groups when you need to enforce content-based access restrictions for readers who authenticate through JWT SSO. **Example scenario:** You sell an enterprise-tier add-on with its own configuration and API docs. Only customers who've purchased that add-on should see those articles — everyone else should just see the standard documentation. **Solution:** 1. Create a reader group in the Document360 private project, granting access only to the enterprise add-on category. 2. Assign readers to this group based on their subscription tier (passed via JWT claims at SSO login). Other common scenarios include: - A partner integration guide visible only to readers from partner organizations, not general customers. - Beta feature documentation restricted to customers enrolled in the beta program. - Multiple customer segments (e.g., different regional product SKUs) who need different views of the same private knowledge base. If your knowledge base is public or all authenticated readers should see the same content, reader group assignment is not required. --- ## Before you begin - Your project must have JWT SSO configured. If you have not set it up yet, see [Configure JWT in Document360](https://docs.document360.com/docs/configuring-the-jwt-sso){target="_blank"}. - At least one reader group must exist in your project. You can create and manage reader groups from **Settings** () > **Users & permissions** > **Readers & groups** > **Reader groups** tab. - You must have a **Project Owner** or **Admin** role to access reader group settings. :::(Info) ( NOTE) Reader group IDs are only available for JWT-configured projects. They are not visible on regular private knowledge base projects without JWT. ::: --- ## Step 1: Get your reader group ID Each reader group in Document360 has a unique ID that you include in the JWT payload to assign readers to that group. 1. Go to **Settings** () > **Users & permissions** > **Readers & groups**. 2. Select the **Reader groups** tab. 3. Locate the reader group you want to use. The **Group ID** is displayed below the group name. 4. Click the **Copy** icon to copy the Group ID to your clipboard.
Can a reader belong to more than one reader group?
Yes. You can include multiple Group IDs in the readerGroupIds array. The reader will inherit the combined access permissions of all assigned groups.
Why can't I see the Group ID in my project?
Reader group IDs are only visible in JWT-configured projects. If your project does not have JWT SSO enabled, the Group ID field will not appear under the Reader groups tab.
What happens if I add an invalid Group ID to the payload?
The token will still be generated, but the invalid Group ID will not map to any group. The reader may not have the expected access restrictions applied. Always verify Group IDs by copying them directly from the portal.
If I remove a Group ID from the payload, does the reader lose access immediately?
No. Changes take effect only after the current token expires. If the token validity is set to 30 minutes, access changes will apply after 30 minutes from the last token issuance.
Why is the Export CSV button disabled on my reader group page?
Document360 does not store reader details for readers authenticated through JWT, since they are authenticated externally in your own application. If a reader group consists entirely of JWT readers, the Export CSV button is disabled for all roles, including Admin and Owner, because there is no portal-stored reader data to export. If your project supports a mix of Normal, SSO, and JWT readers, Normal and SSO reader data can still be exported, but JWT reader data cannot. See the article on Export reader group for more detail on this limitation.