---
title: "Remove a configured SAML SSO"
slug: "removing-a-configured-saml-sso"
description: "A configured SAML Single Sign-On (SSO) can be updated at any time or easily removed with just a click of a button. You can then easily configure another standard of SSO available."
tags: ["SAML"]
updated: 2026-06-18T09:48:52Z
published: 2026-06-18T09:48:52Z
canonical: "docs.document360.com/removing-a-configured-saml-sso"
---
> ## Documentation Index
> Fetch the complete documentation index at: https://docs.document360.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Remove a configured SAML SSO
Removing a SAML SSO configuration from Document360 permanently deletes it along with all associated user accounts. This action cannot be undone.
:::(Warning) ( CAUTION)
When you delete an SSO configuration, all users associated with that configuration will also be deleted. Ensure you have reviewed the impact on your team before proceeding.
:::
## When you might need to remove a SAML SSO configuration
- You are switching to a different Identity Provider.
- You are replacing an incorrectly configured SSO setup.
- You are decommissioning SSO for a project.
---
## Before you remove
- Notify affected users in advance. Once deleted, they will lose access immediately.
- If you plan to reconfigure SSO with a new provider, have the new configuration ready before removing the existing one to minimize disruption.
- If the configuration is a parent with child projects inheriting its SCIM settings, removing it will affect those child projects. Review your inheritance setup before proceeding.
---
## Remove a SAML SSO configuration
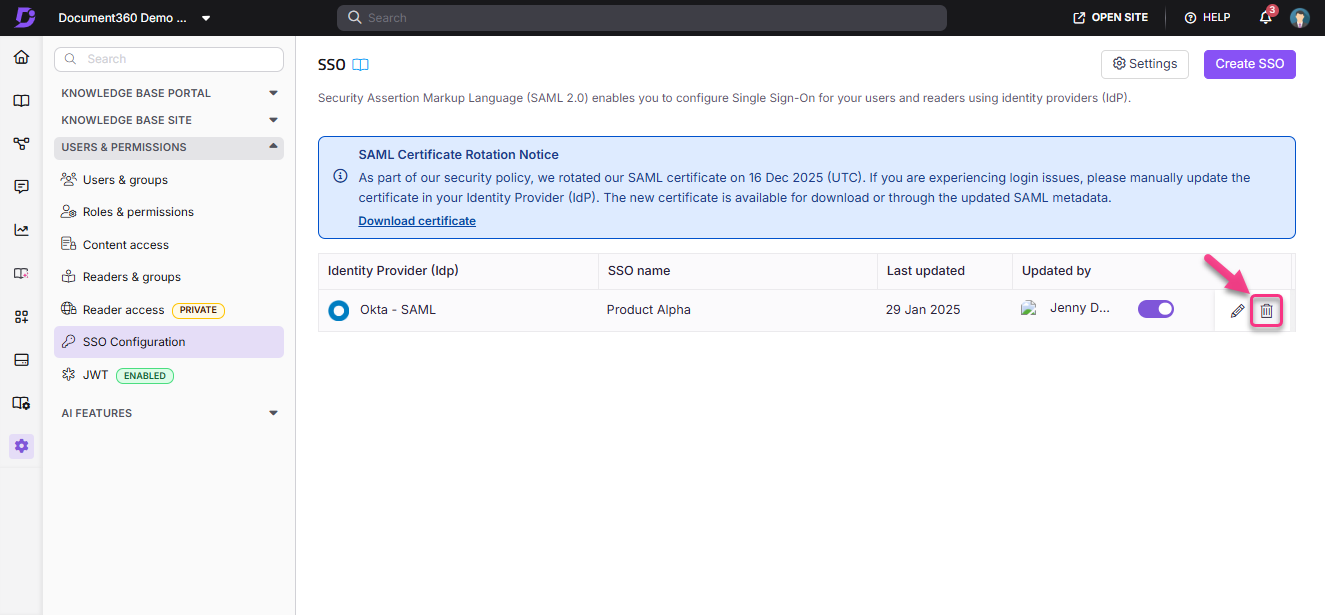
1. Navigate to **Settings () > Users & permissions > SSO Configuration**.
2. Hover over the SSO configuration you want to delete and click the **Delete** () icon.
3. A **Delete SSO confirmation** dialog will appear.
4. Click **Proceed** to permanently delete the SSO configuration.
The SSO configuration and all associated user accounts are now deleted.
---
## What happens after deletion
- All users who authenticated via the deleted SSO configuration are removed from Document360.
- Users will no longer be able to log in using their SSO credentials for that configuration.
- The Document360 login page will be restored as the default login method if no other SSO configuration is active.
- If you had the Document360 login page disabled, re-enable it before removing SSO to avoid locking all users out.
:::(Info) ( NOTE)
To reconfigure SSO after deletion, see the relevant provider setup guide: [Okta](https://docs.document360.com/docs/saml-sso-with-okta){target="_blank"}, [Entra](https://docs.document360.com/docs/saml-sso-with-entra){target="_blank"}, [Google](https://docs.document360.com/docs/google-sso-saml-configuration){target="_blank"}, [OneLogin](https://docs.document360.com/docs/saml-sso-with-onelogin){target="_blank"}, [ADFS](https://docs.document360.com/docs/saml-sso-with-adfs){target="_blank"}, or [other providers](https://docs.document360.com/docs/saml-sso-with-other-configurations){target="_blank"}.
:::
## Related
- [SAML SSO with Entra](/saml-sso-with-entra.md)
- [SAML SSO with Google](/google-sso-saml-configuration.md)