Sign out SSO users automatically after a period of inactivity, so that no one else can use an unattended session in the Knowledge base portal. You turn on an idle timeout in your SAML or OpenID Connect configuration and choose how long a session can stay inactive. The timeout applies only to SSO users. It doesn't affect people who sign in with a Document360 email and password.
When to sign out idle SSO users
- Your knowledge base has confidential or internal content, and your security policy limits how long an inactive session can stay open.
- People use shared or public computers, where a session might be left open.
Before you begin
- Your project must have SSO configured with SAML or OpenID Connect.
- You need the Owner or Admin project role to edit SSO configurations.
How to sign out idle SSO users
- Go to Settings () > Users & Permissions > Enterprise SSO.
- Hover over the SSO configuration you want to update and click the Edit () icon.
- In the configuration panel, go to the More settings tab.
- Turn on the Idle session SSO timeout toggle.
- In the Timeout duration field, enter the idle time in HH:MM (hours:minutes) format, for example
01:30. The default is 2 hours, and the maximum is 23 hours and 59 minutes. - Click Save.
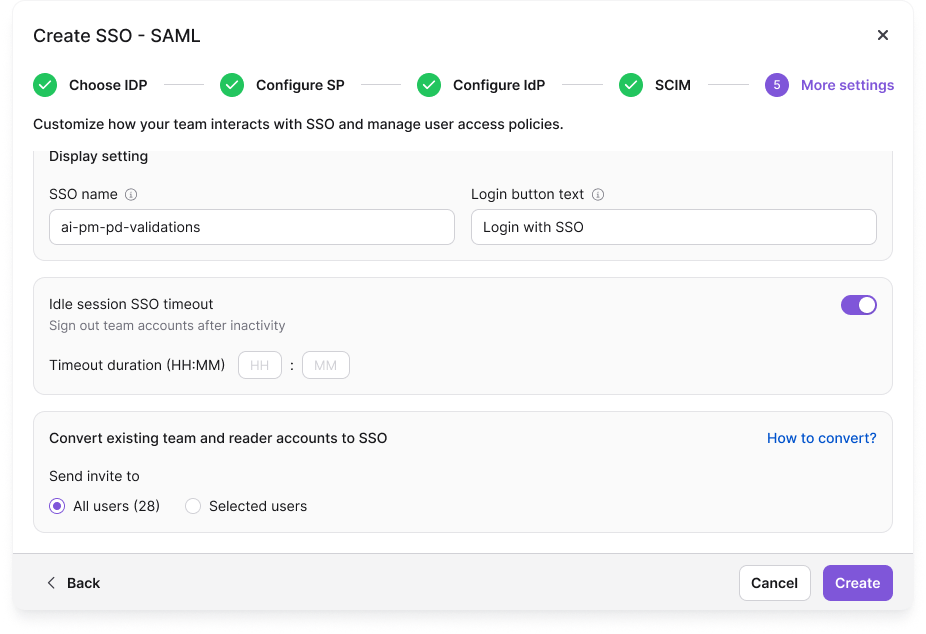
SSO users who stay inactive for the duration you set are signed out and must sign in again with SSO.
Limits and limitations
| Item | Limit |
|---|---|
| Who is signed out | SSO users only. Users who sign in with a Document360 email and password aren't affected. |
| Default timeout | 2 hours |
| Maximum timeout | 23 hours and 59 minutes |
Best practices
- Match the timeout to how sensitive your content is. Use a shorter timeout for confidential content and a longer one where convenience matters more. A shorter timeout is more secure but makes people sign in more often.
- Keep the default if it fits. If 2 hours meets your organization's requirements, you don't need to change it.
- Tell your SSO users about the timeout. Let them know that inactive sessions end automatically, so they know why they were signed out.
- Set the timeout on each configuration. The setting is part of each SSO configuration, so check it on every configuration in your project.
Related articles
More on SSO configurations:
FAQ
What happens when a user is signed out because of inactivity?
The user must sign in again with SSO to get back into the Knowledge base portal.
Does the idle timeout sign out users who don't use SSO?
No. The timeout applies only to SSO users. Users who sign in with a Document360 email and password aren't affected.