Remove a SAML SSO configuration when you switch identity providers, replace a misconfigured setup or stop using SSO for a project. Deleting a configuration from Document360 is permanent: it deletes the configuration and all user accounts associated with it, and you can't undo it.
When you delete an SSO configuration, all users associated with that configuration are also deleted. Review the impact on your team before you continue.
When to remove a SAML SSO configuration
- You are switching to a different identity provider.
- You are replacing an incorrectly configured SSO setup.
- You are decommissioning SSO for a project.
If you only need to stop people signing in with this configuration, you can turn it off instead of deleting it.
Before you begin
- You have the Owner or Admin project role. Only these roles can configure SSO in Document360.
- Check how people will sign in after the removal. If this is the only active SSO or JWT configuration and the Document360 login page is deactivated, Document360 blocks the deletion. Turn the default login page back on, or enable another configuration, first.
- Notify affected users in advance. They lose access as soon as you delete the configuration.
- If you plan to move to a new provider, have the new configuration ready before you remove the existing one.
- If the configuration is a parent with child projects inheriting its SCIM settings, removing it affects those child projects. Review your setup in Mapping an existing SSO configuration to other projects before you continue.
How to remove a SAML SSO configuration
- Go to Settings () > Users & Permissions > Enterprise SSO.
- Hover over the SSO configuration you want to delete and click the Delete () icon.
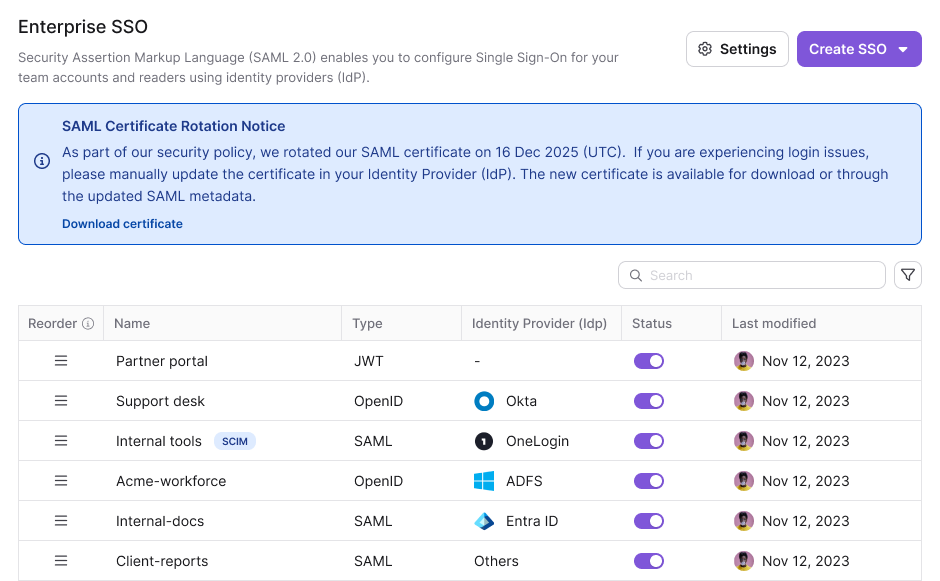
- In the Delete SSO confirmation dialog, click Proceed.
Document360 deletes the SSO configuration and all associated user accounts.
If this is the only active SSO or JWT configuration and the default login page is disabled, Document360 doesn't delete it and shows this message:
This is the only active SSO or JWT configuration and the default login page is disabled, so turning it off or deleting it would lock everyone out. Enable another configuration, or turn the default login page back on, first.
What happens after you remove
- All users who signed in through the deleted SSO configuration are removed from Document360.
- People can no longer sign in with their SSO credentials for that configuration.
- Document360 doesn't change your login page settings. People sign in through the default login page or any other active SSO or JWT configuration.
To use SAML SSO again, create a new configuration with your provider's setup guide: Okta, Entra, Google, OneLogin, ADFS or other providers.
Related articles
- Deactivating Document360 login page
- Mapping an existing SSO configuration to other projects
- Remove a configured OpenID SSO
- SAML
FAQ
Can I restore a deleted SAML SSO configuration?
No. Deletion is permanent. To use SAML SSO again, create a new configuration with your provider's setup guide.
Why can't I delete my SAML SSO configuration?
Document360 blocks the deletion when the configuration is the only active SSO or JWT configuration and the default login page is disabled, because deleting it would lock everyone out. Turn the default login page back on, or enable another configuration, and try again.