Set up SAML SSO with Google Workspace so your users and readers sign in to Document360 with their Google accounts, without a separate password. You create a custom SAML app in the Google Admin console and then complete the SSO configuration in Document360. Google Workspace does not support SCIM provisioning with Document360, so you add and remove users and readers in Document360.
Only users with the Owner or Admin project role can configure SSO in Document360.
When to use Google Workspace with SAML SSO
Use this setup when:
- Your organization already manages accounts in Google Workspace and you want people to use those accounts to sign in.
- You want users to sign in to the knowledge base portal and readers to sign in to the knowledge base site with the same Google account.
- You want people to open Document360 directly from their Google apps (IdP-initiated sign-in).
- You manage user and reader accounts in Document360 yourself and don't need automatic provisioning.
| Capability | Supported |
|---|---|
| User (knowledge base portal) authentication | Yes |
| Reader (knowledge base site) authentication | Yes |
| IdP-initiated sign-in | Yes |
| SCIM provisioning | No |
| SSO configuration inheritance (parent-child projects) | Yes (SSO settings only, not SCIM) |
SCIM provisioning is not supported when Google Workspace is configured as your Identity Provider. User and reader management must be handled manually in Document360. To add people, read Inviting or Adding SSO users and Managing SSO readers and reader groups.
Before you begin
- You need an active Google Workspace account with administrator access. If you need one, sign up at workspace.google.com.
- You need the Owner or Admin role in your Document360 project.
- Open Document360 and the Google Admin console in two browser tabs. You switch between them during setup.
How to set up SAML SSO with Google Workspace
Step 1: Start the SSO configuration in Document360
- Go to Settings () > Users & Permissions > Enterprise SSO.
- Select Create SSO.
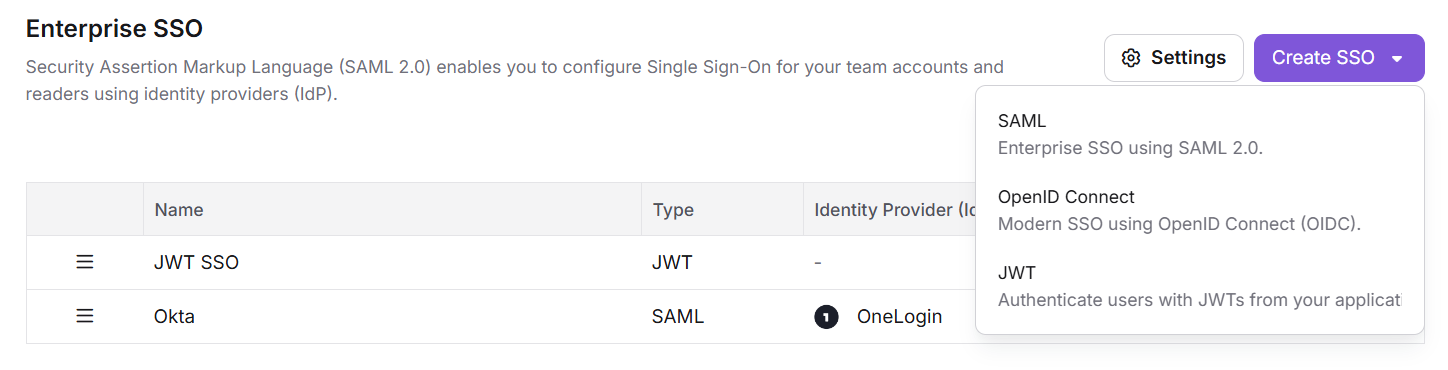
- Select SAML (Enterprise SSO using SAML 2.0).
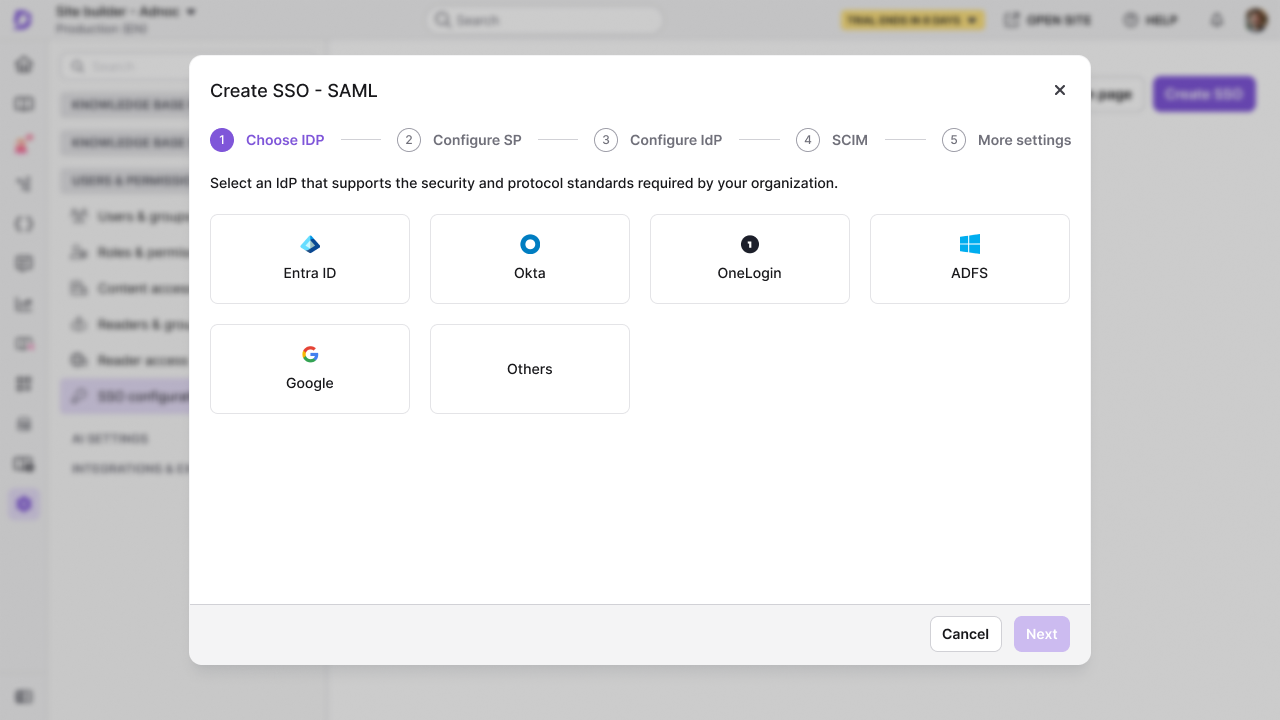
- Select Google as your identity provider.
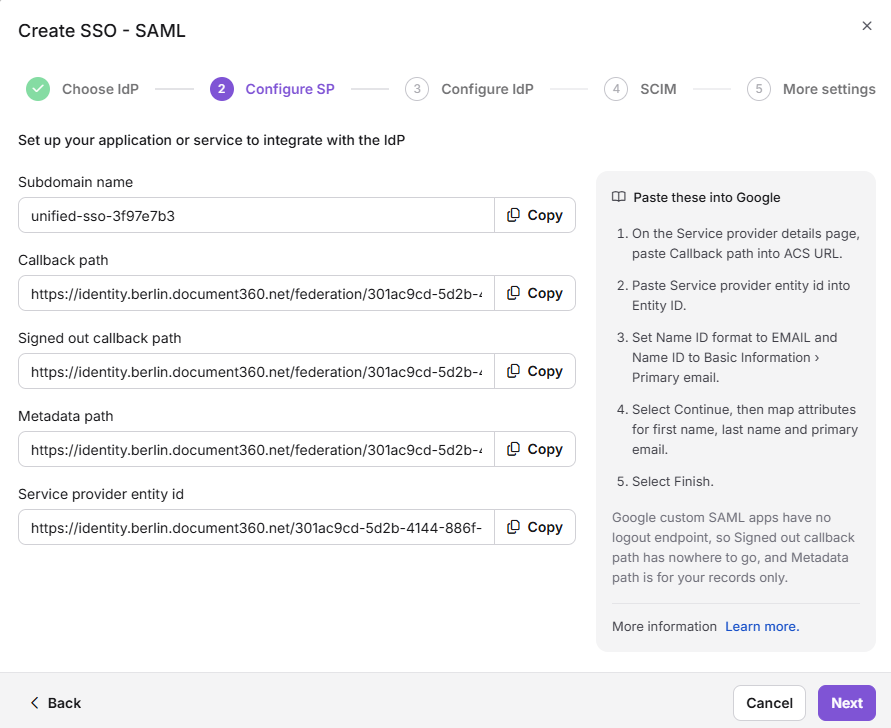
The Configure SP step opens and shows the Callback path and Service provider entity ID you enter in Google Workspace. Keep this tab open.
Step 2: Create a custom SAML app in Google Workspace
Add the app
- On the Google Workspace admin console home page, click Apps and select SAML apps.
- Click Add app and, in the dropdown, select Add custom SAML app.
- In App details, enter a name for your app and click Continue.
Note the IdP details and download the certificate
- On the next page, note the SSO URL and Entity ID. You enter them in Document360 in Step 4.
- In the Certificate section, click the download icon to save the certificate in
.pemformat. You upload this file in Document360 in Step 4.
Enter the Document360 parameters
-
Copy these values from the Document360 Configure SP step into the Google custom SAML app:
Google custom SAML app Document360 ACS URL Callback path Entity ID Service provider entity ID -
In Name ID format, select EMAIL.
-
In Name ID, select Basic Information > Primary email.
-
Click Continue.
Add attribute mappings
-
Add these mappings from Google Directory attributes to app attributes. Click Add Mapping for each one.
Google Directory attributes App attributes Primary email name Primary email email Primary email urn:oasis:names:tc:SAML:2.0:nameid -
Click Finish.
Google Workspace creates the custom SAML app.
Step 3: Turn on the app for your users
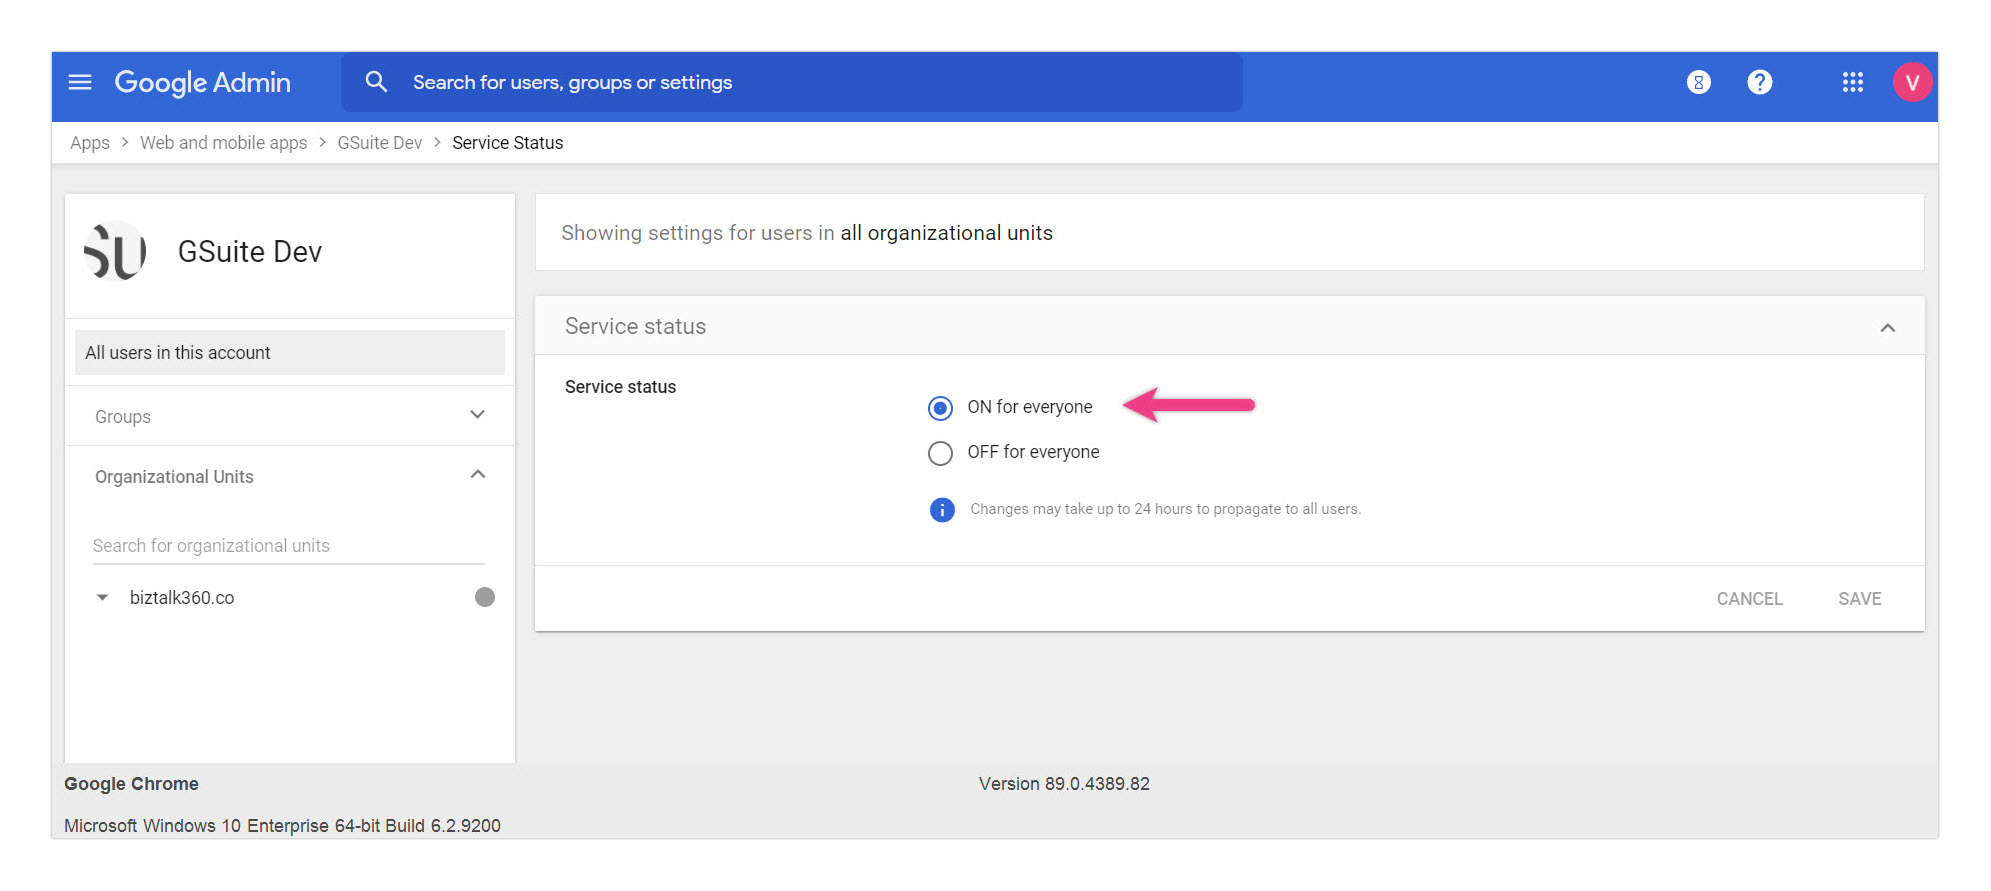
- In the app's User access section, the Service status is set to OFF for everyone by default.
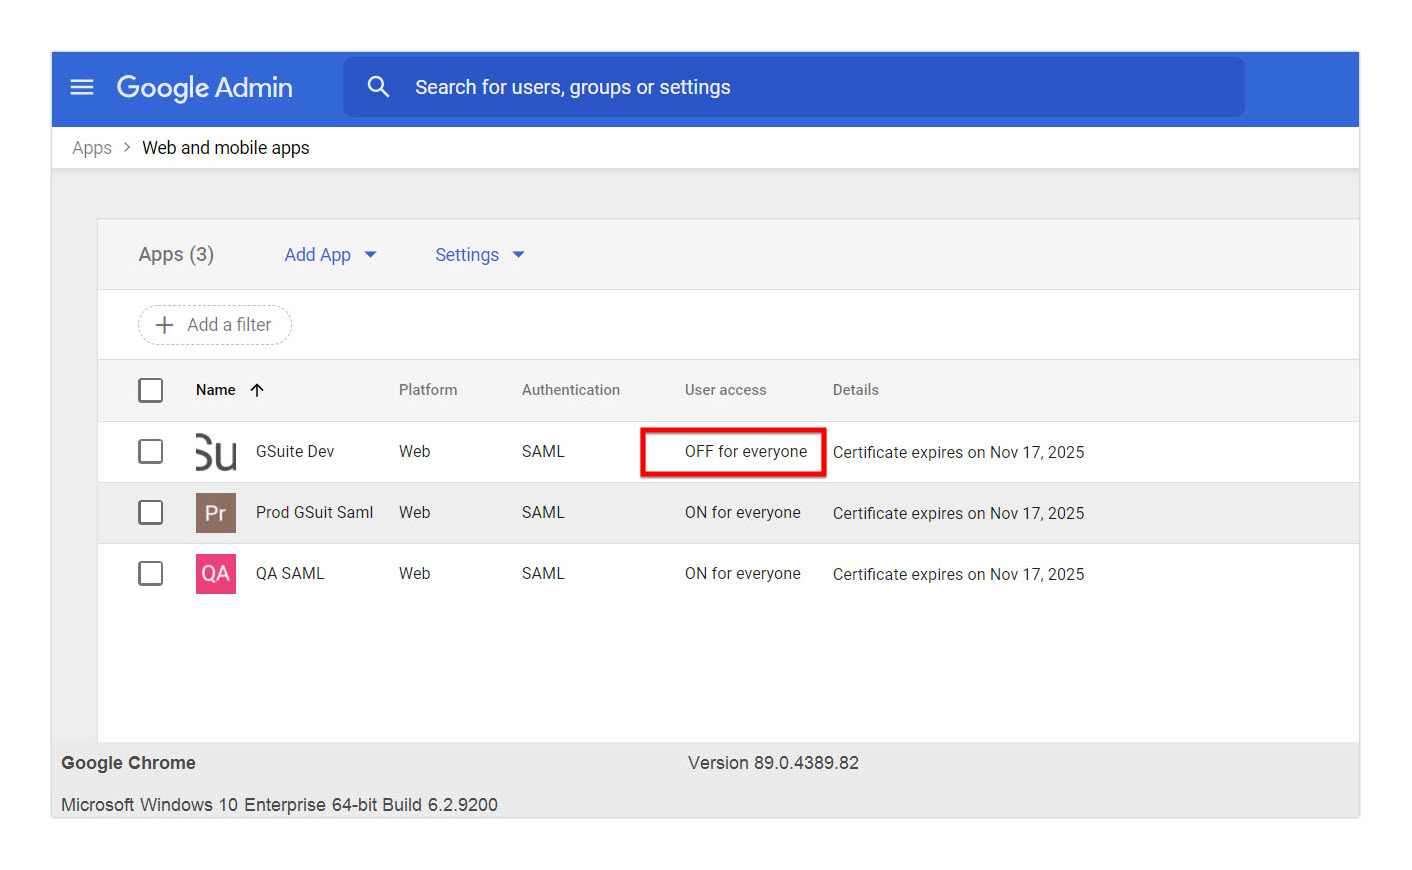
- Change it to ON for everyone so people can sign in with this app.
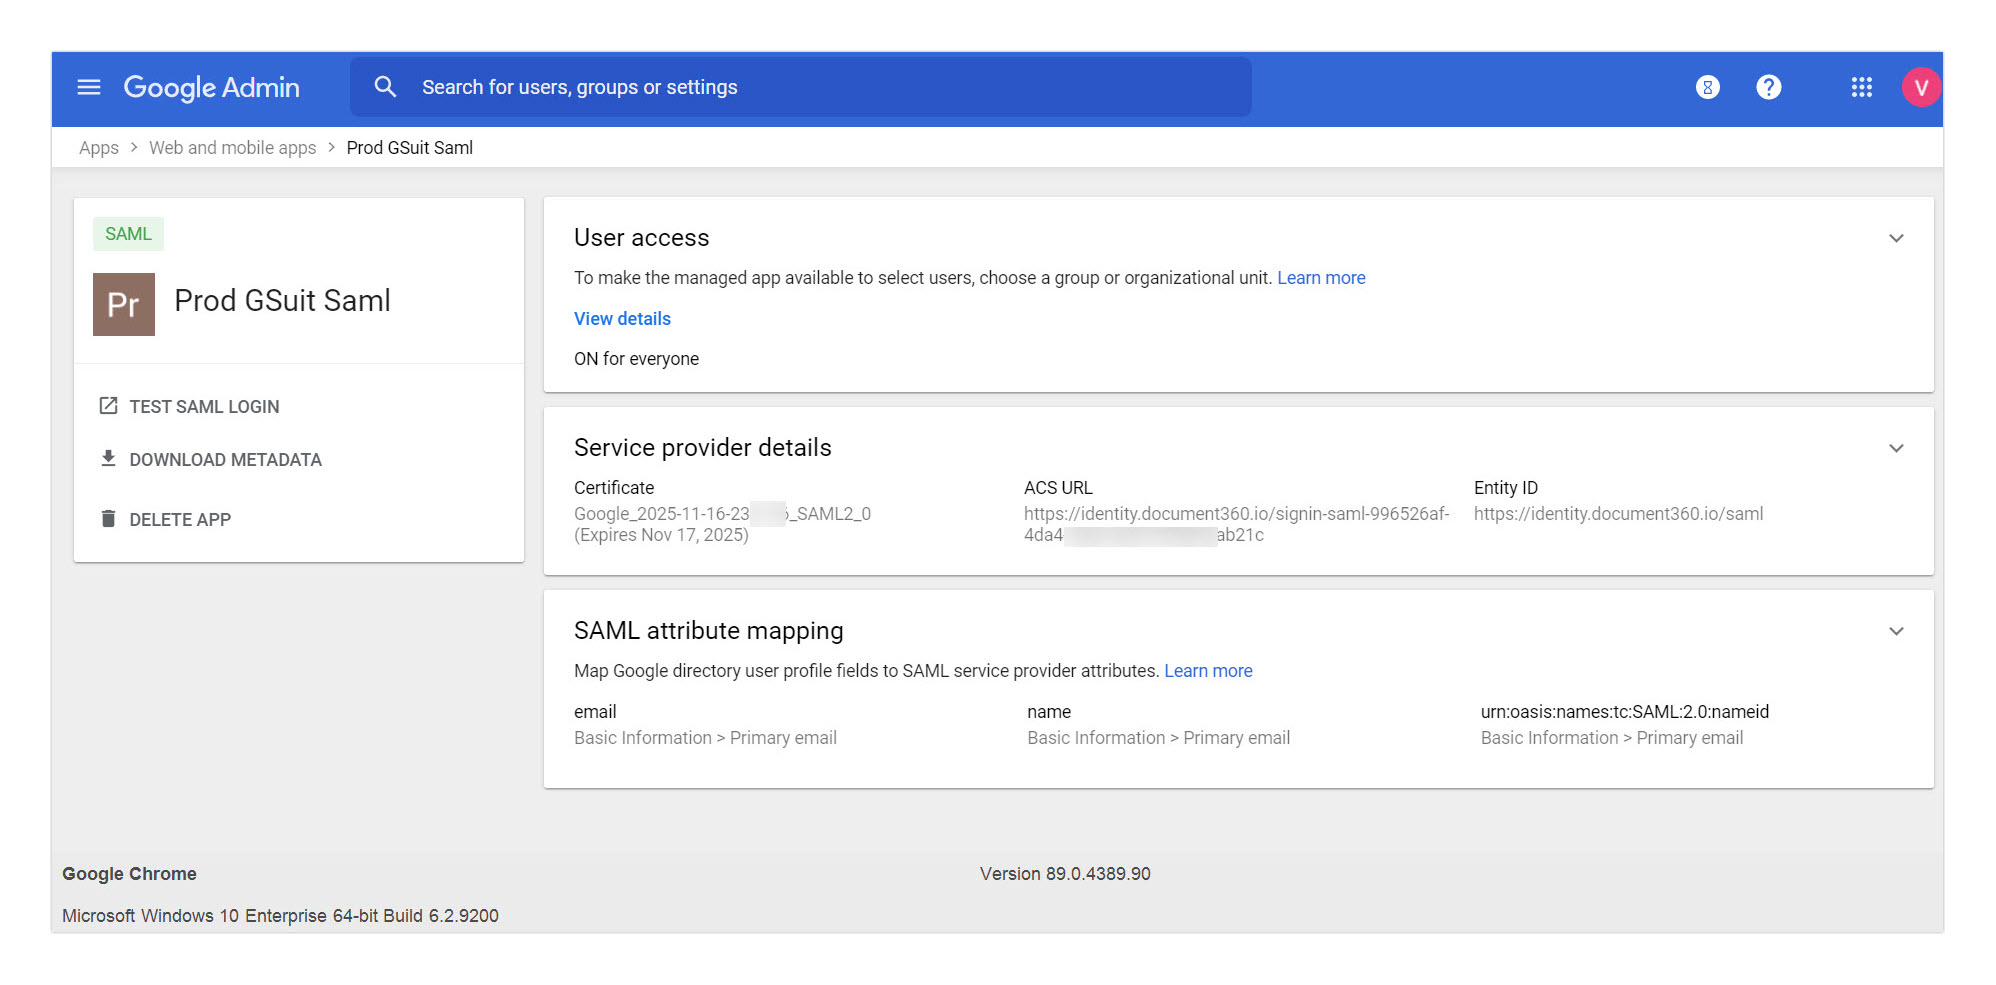
Your finished SAML app looks like this:
Step 4: Enter the Google details in Document360
-
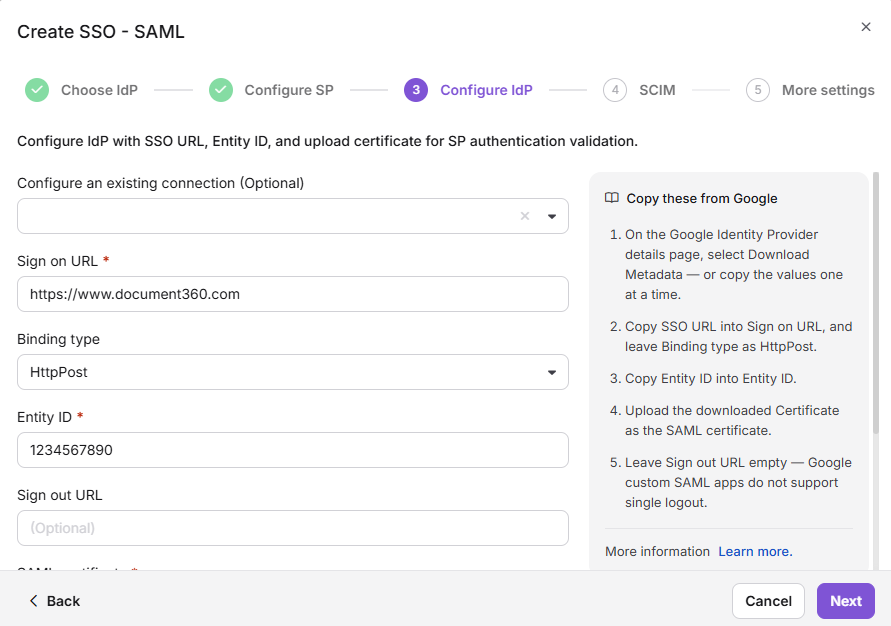
Switch to the Document360 tab and click Next to go to the Configure IdP step.
-
(Optional) To reuse an SSO configuration you already created, select it in Configure an existing connection. This configuration becomes the child and inherits the parent's settings. To learn more, read Inherit from another application.
-
Enter the details you noted from the Google custom SAML app:
Document360 Google custom SAML app Sign on URL SSO URL Entity ID Entity ID SAML certificate Certificate (upload the .pem file downloaded from Google) -
To let people open Document360 from their Google apps without visiting the Document360 login page first, turn on Allow IdP initiated sign in.
- Click Next. The SCIM step opens.
Step 5: Skip the SCIM step
SCIM provisioning is not supported when Google is configured as your Identity Provider (IdP) in Document360. This applies to new Google configurations and to configurations that inherit from an existing SSO configuration that uses Google.
Click Next to continue.
Step 6: Name the configuration and create it
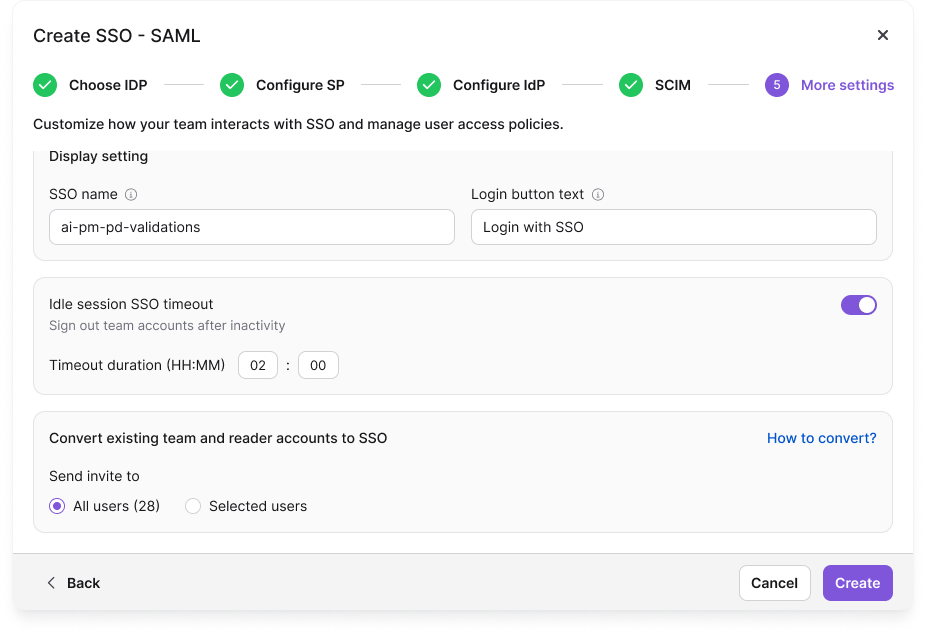
- In SSO name, enter a name for the SSO configuration.
- In Login button text, enter the text for the sign-in button. The default text is Login with SSO.
- (Optional) To switch existing accounts to this SSO configuration, turn on Convert existing team and reader accounts to SSO. Then, under Send invite to, select All users or Selected users. Each existing account is converted to SSO; Document360 does not create a second account.
- Click Create.
The configuration appears in the Enterprise SSO list.
Auto assign reader group appears only when you edit an existing SSO configuration. It is hidden while you create a new one. To learn more, read Managing SSO readers and reader groups.
Step 7: Test the sign-in
- Open the Document360 login page in a private browser window.
- Enter your email address or subdomain and click Login with SSO (or the button text you set in Step 6).
- Sign in with a Google Workspace account that has access to the app and has a user or reader account in Document360.
You're signed in to Document360. If sign-in fails, read SSO login issues and SAML SSO issues.
Inherit from another application
If you already have an SSO configuration in another project, you can inherit it instead of entering the same details again. On the Configure IdP step, select the parent SSO configuration in Configure an existing connection. The current project becomes the child and inherits the relevant settings from the parent.
Once the SSO configuration is created, the settings are inherited from the parent application and cannot be modified in the child application. SCIM settings cannot be inherited when Google is the IdP, even if the parent configuration has SCIM enabled.
View and manage SSO readers in Document360
Because Google Workspace does not provision people through SCIM, you add, update, and remove users and readers in Document360. To find readers and manage their content access:
- Go to Settings () > Users & Permissions > Readers & groups.
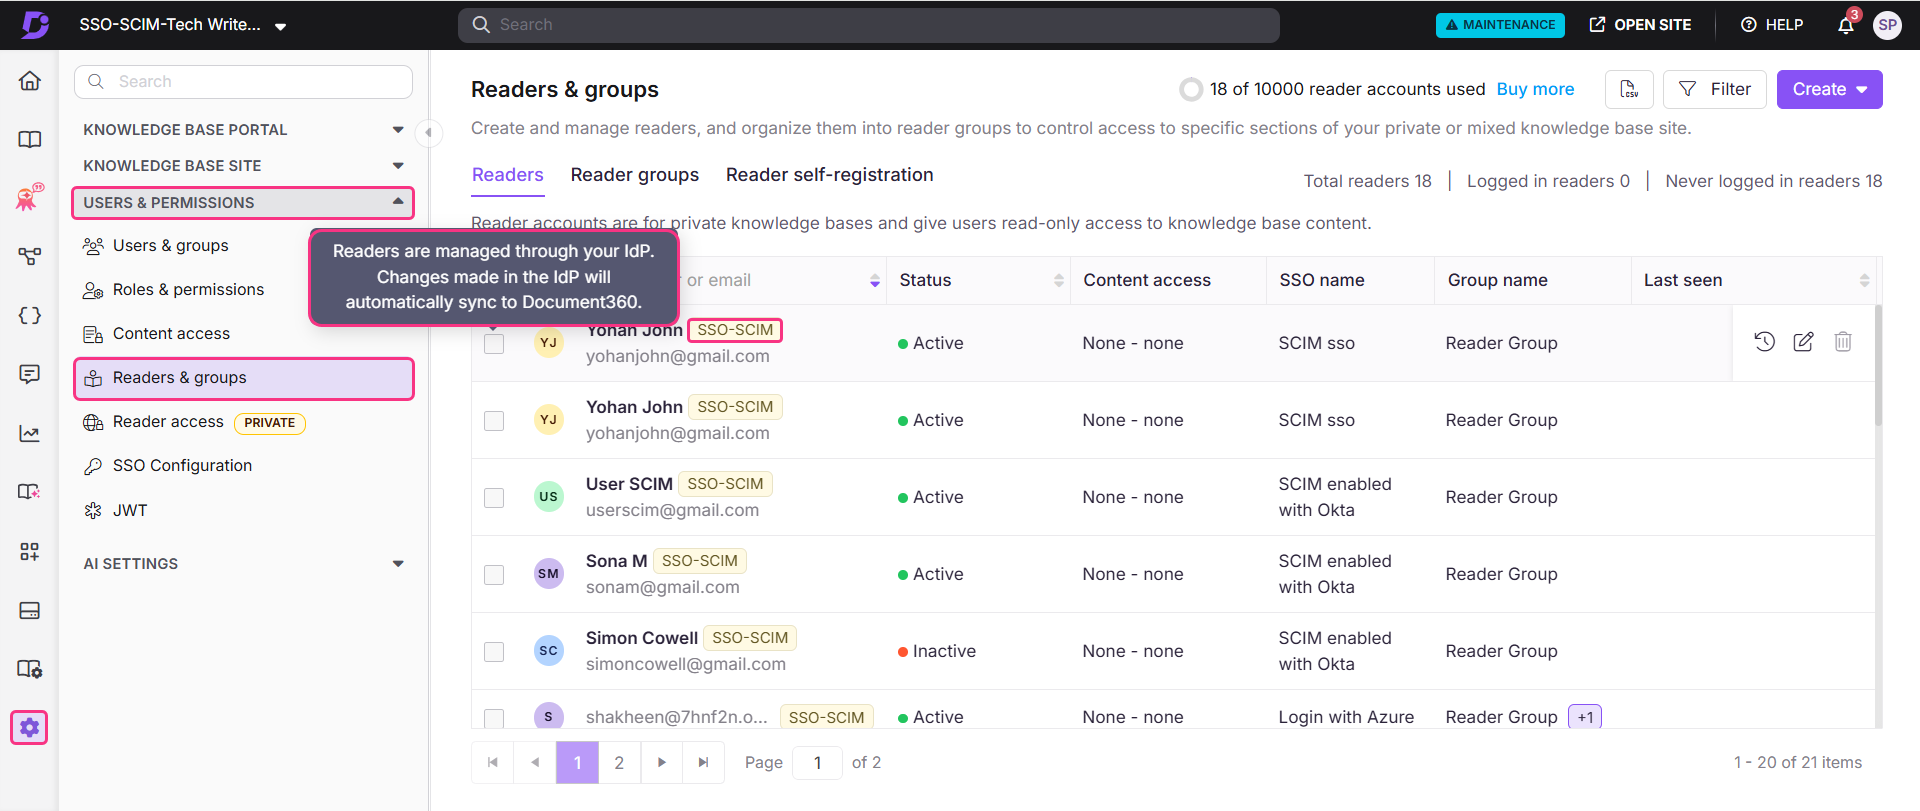
- Select a reader to open their reader profile.
- Click Manage Content Access.
- Choose the access level from the dropdown and click Update.
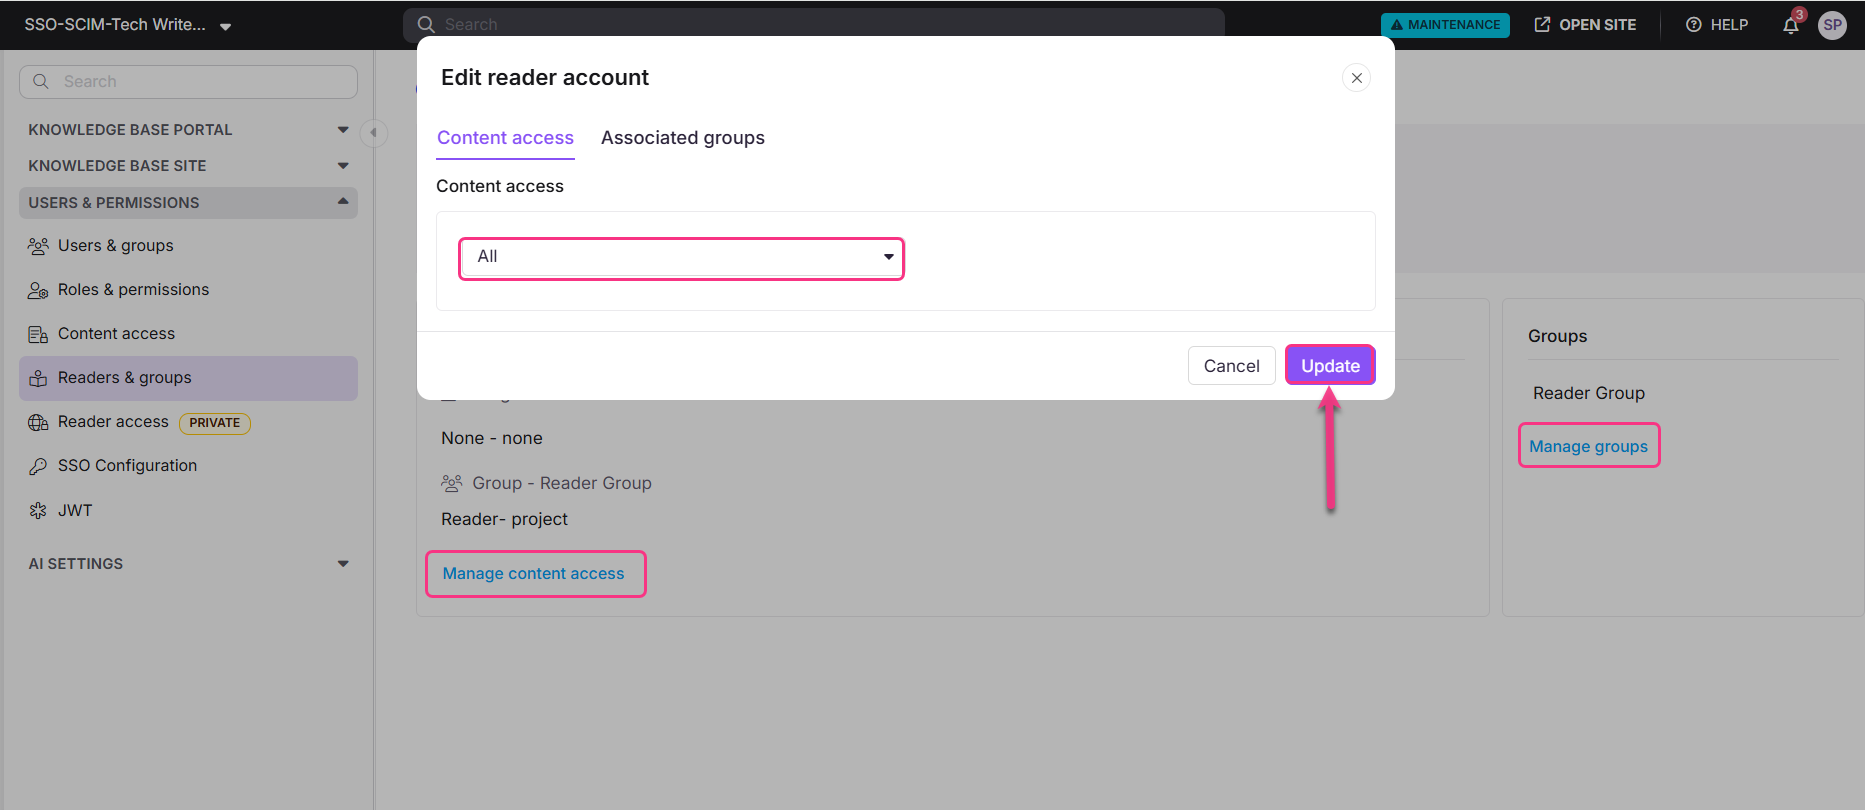
The default content role assigned to any new user, reader, or group is based on what was configured during SCIM provisioning setup. Permissions are set to None by default and can be updated at any time. To manage a reader's groups, click Manage groups under the Reader Group section.
When SCIM is enabled, editing a user's name or deleting a user directly in Document360 is disabled, as these actions must be managed through your IdP to keep both platforms in sync. You can only manage content access from Document360.
Limits and limitations
| Limitation | Details |
|---|---|
| SCIM provisioning | Not supported with Google Workspace. Add and remove users and readers in Document360. |
| Inheritance | You can inherit SSO settings from a parent configuration, but not SCIM settings. |
| App access in Google | The custom SAML app is OFF for everyone by default. People can't sign in until you turn it on. |
| Auto assign reader group | Available only on existing SSO configurations. Hidden when you create a new configuration. |
| Last active configuration | If this is the only active SSO or JWT configuration and the default login page is disabled, Document360 blocks you from turning it off or deleting it, with the message: "This is the only active SSO or JWT configuration and the default login page is disabled, so turning it off or deleting it would lock everyone out. Enable another configuration, or turn the default login page back on, first." |
Best practices
- Turn on the app before you test SSO. The Google SAML app service status is OFF for everyone by default. Change it to ON for everyone before people sign in with SSO.
- Save the .pem certificate securely. Download and store the Google certificate before you complete the configuration in Document360. You will not be prompted to download it again.
- Plan manual user management. Because SCIM is not supported, decide how you will add, update, and remove users and readers in Document360 when you use Google as your IdP.
- Consider Okta or Entra if you need SCIM provisioning. If automated user lifecycle management is a requirement, configure SSO using Okta or Microsoft Entra as your identity provider instead.
FAQ
Why is SCIM provisioning not supported for Google IdP?
Document360's SCIM provisioning requires specific provisioning capabilities that Google Workspace does not support in the same way as Okta or Microsoft Entra. If you need automated user provisioning, consider configuring SSO using Okta or Microsoft Entra as your identity provider.
Can I inherit SCIM settings from a parent project when using Google as my IdP?
No. While other SSO configuration settings can be inherited from a parent project, SCIM settings cannot be inherited when Google is configured as the Identity Provider. This applies both to new configurations and to inherited configurations where the parent uses Google as the IdP.
What happens to existing Document360 accounts when I configure Google SSO?
Nothing, unless you turn on Convert existing team and reader accounts to SSO in Step 6 and choose All users or Selected users. The accounts you select are converted to SSO; Document360 does not create a second account. To convert accounts later, read Convert user to SSO and Convert reader to SSO.